Podcasts
Your No-Show Problem Is a Communication Problem
67% of patients leave providers because of poor communication. Here's how to audit your workflows, close the gaps, and stop losing revenue to a fixable problem.
Read More

Break-fix IT is a gamble with your EHR, phones, and claims. Learn when managed IT pays off and what to ask any provider. Let's talk about your setup.
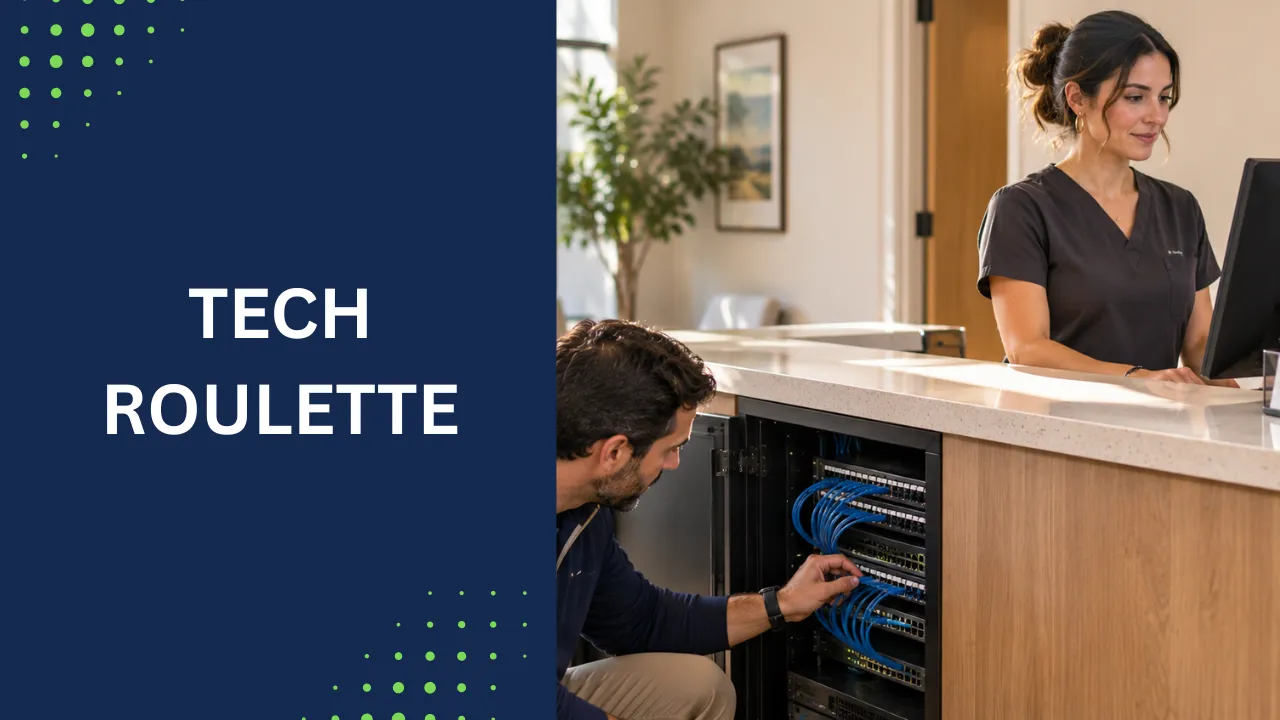
It's 9:15 on a Tuesday and the router goes down. Your front desk can't open the EHR, the phones are silent, and three patients are calling to confirm appointments nobody can see. Someone texts "the computer guy," and now the whole practice waits.
That scene is the break-fix model in action. Something breaks, you call someone, and you pay for the repair plus every minute your practice couldn't operate.
Brandon Seigel framed it bluntly on a recent episode of the Private Practice Survival Guide podcast: relying on break-fix IT is like putting a thousand dollars on black. Maybe it works out this month, but the odds catch up with every practice eventually.
Break-fix is ad hoc by design. There's no monitoring, no standard setup, and no one watching your systems until you call.
Managed IT works the other way around. Yves Martin, an IT and cybersecurity specialist who works with private practices, compares it to pulling into your garage every night and having a team of mechanics check the oil and tires before you notice a problem. A managed provider installs monitoring agents on your machines that flag issues early, like a hard drive nearing capacity or activity that looks suspicious, so they can fix it before you go down.
The difference isn't the repair. It's whether you're still operating while the problem gets solved.
Most owners assume managed IT is for large groups. Martin's view is that it becomes worth it at three to five team members.
At that size you already have multiple machines, multiple logins, separate email accounts, and different access roles. Every one of those is a door, and in a HIPAA environment, an unmanaged door is a liability.
He sees the same pattern whenever his team takes over a new office. Shared logins, laptops bought off the shelf and set up by whoever was available, personal browsers installed on clinical machines, and a different desktop background on every screen.
That last one sounds minor, but a standard, practice-branded setup sends a clear signal: these are business machines, used for business purposes. That mindset does real work for your compliance culture, the same way a clear onboarding checklist does when you build out your fractional HR systems.
Martin puts the typical range at roughly $175 to $275 per user per month. Where you land depends on what's covered.
At the lower end, expect device support, a monitoring agent, security software, and basic alerts. As you move up, you add services like backup and 24/7 proactive security monitoring.
That second tier matters more than most owners realize. If an employee clicks a phishing link at noon, the attacker may wait until 3:00 a.m. to move, when nobody is watching. Round-the-clock monitoring shuts that down while you sleep, and the worst outcome is one locked-out employee the next morning instead of a breach.
Brandon added a warning about quotes. A provider charging $100 per user might be doing little more than installing antivirus software and calling it a cybersecurity program, so ask for a breakdown of what's software and what's actual people and time.
You don't need to speak tech to evaluate an IT partner. You need to ask the right questions and listen closely to how they answer.
Ask for references and follow up on them. If that's not possible, start with a small project and see how they handle it.
Switching from break-fix isn't the only move. Practices that already have a managed provider benefit from a periodic third-party vulnerability scan.
These scans confirm your provider is doing what they promised and catch gaps, like a monitoring agent that never got installed on the newest workstation. A good provider welcomes that second set of eyes.
There's also a continuity argument. A solo IT person can disappear, change careers, or simply stop answering, and take everything they know about your systems with them. A managed team documents your setup so that knowledge stays with your practice.
When your systems go down, the costs stack up fast. No EHR means no documentation, no phones means no scheduling, and nothing gets submitted to payers.
That last point is easy to miss. Every hour of downtime pushes back claim submission and payment posting, which is exactly the daily rhythm strong medical billing depends on.
Technology isn't the part of your practice you want to gamble with. Treat it like the infrastructure it is, and build accountability into it the same way you would any other part of your operations.
If you want a partner to pressure-test the systems behind your practice, call 877-561-9967 to book a Discovery Call. Let's see if we're the right fit.